Executive Summary: The Invisible Toll of "Free" Streaming
For years, cybersecurity researchers have raised alarms regarding the proliferation of cheap, off-brand Android TV boxes sold across mainstream e-commerce platforms. These inexpensive streaming devices promise consumers a tempting proposition: unlimited access to premium channels, pay-per-view live sports, and vast libraries of on-demand content for a negligible, one-time fee—bypassing traditional monthly subscription models altogether.
However, security experts have long warned that these devices harbor a sinister trade-off, secretly monetizing the consumer’s domestic internet connection by routing stranger traffic through residential proxies.
Now, groundbreaking telemetry analysis from cybersecurity firm Bitsight reveals a far more insidious layer to this global infrastructure. Beyond merely acting as silent backdoors for proxy traffic, a staggering number of these generic streaming sticks—specifically the widely popular H96 brand—are pre-programmed to participate in a sophisticated, automated ad-fraud operation.
Operating under the guise of legitimate mobile devices, tens of thousands of these compromised TV boxes are weaponized to visit AI-generated websites, systematically clicking on fraudulent advertisements. Orchestrated by a mainland Chinese entity known as the Fengwo Group, this operation bridges low-code software development tools, visual AI reasoning systems, and mass-market consumer electronics to siphon an estimated $50,000 or more per day from unsuspecting digital advertising networks.
Chronology of an Investigation: Unmasking the H96 Ad-Fraud Network
The exposure of this complex cybercriminal apparatus began not with high-tech forensic malware reverse-engineering, but through a piece of digital real estate: an expired domain name.
The Expired Domain Discovery
Pedro Falé, a threat researcher at Bitsight, made the breakthrough discovery while investigating telemetry data associated with the H96 streaming device family. The domain name in question had previously been utilized by the manufacturers to harvest telemetry data—periodically pinging home to collect extensive hardware diagnostics and the complete inventory of installed applications from tens of thousands of consumer TV boxes active across the globe.
When the domain registration lapsed, Falé scooped it up. By peering inside the incoming traffic funneled toward the domain, he uncovered an anomaly that defied standard IoT architecture.
The Mobile Phone Illusion
Upon inspecting the data streams of the H96 devices phoning home, Falé discovered that nearly all of the connected TV boxes were falsely reporting their device classifications. Instead of identifying as fixed-location Android TV units, the telemetry packets claimed the devices were mobile smartphones manufactured by household tech giants such as Samsung, Vivo, Huawei, and Xiaomi.
"We noticed something was wildly wrong," Falé noted in an interview. "Multiple devices reporting to this factory Android TV Box backdoor were ‘phones.’"
A deeper forensic inspection of the applications residing on these streaming boxes revealed two identical, pre-installed apps tied to a mainland Chinese entity: Zhejiang Fengwo IoT Technology Ltd, operating under the umbrella of the Fengwo Group. Founded in 2019, the Fengwo Group had quietly registered multiple patents that matched the precise behavioral mechanics embedded within these applications.
Mechanics of the Fraud: AI, Blockly, and the "TV On/Off" Switch
The Fengwo Group’s infrastructure represents a masterclass in industrializing cybercrime through automation and low-code operational efficiencies.
Low-Code Cybercrime via Blockly
Bitsight’s analysis revealed that the enterprise leverages a proprietary adaptation of Blockly—a Google-built visual programming language originally designed to teach children the foundational logic of software coding.
By integrating Blockly into an internal wiki platform, Fengwo Group’s operators bypassed the need for large teams of elite software engineers. Instead, low-skilled operators could simply drag-and-drop blocks of code together inside a visual web editor to construct custom ad-fraud routines. Once saved, these routines automatically compiled into JavaScript and uploaded to Amazon S3 cloud storage buckets.
As Bitsight’s published report highlights, this structural design drastically reduces operational overhead:
Only a small tier of highly skilled engineers is required to build baseline template execution-unit images.
Lower-skilled workers can rapidly assemble functional fraud tasks from those templates without understanding the underlying technicalities.
AI Digital Humans and Synthetic Web Ecosystems
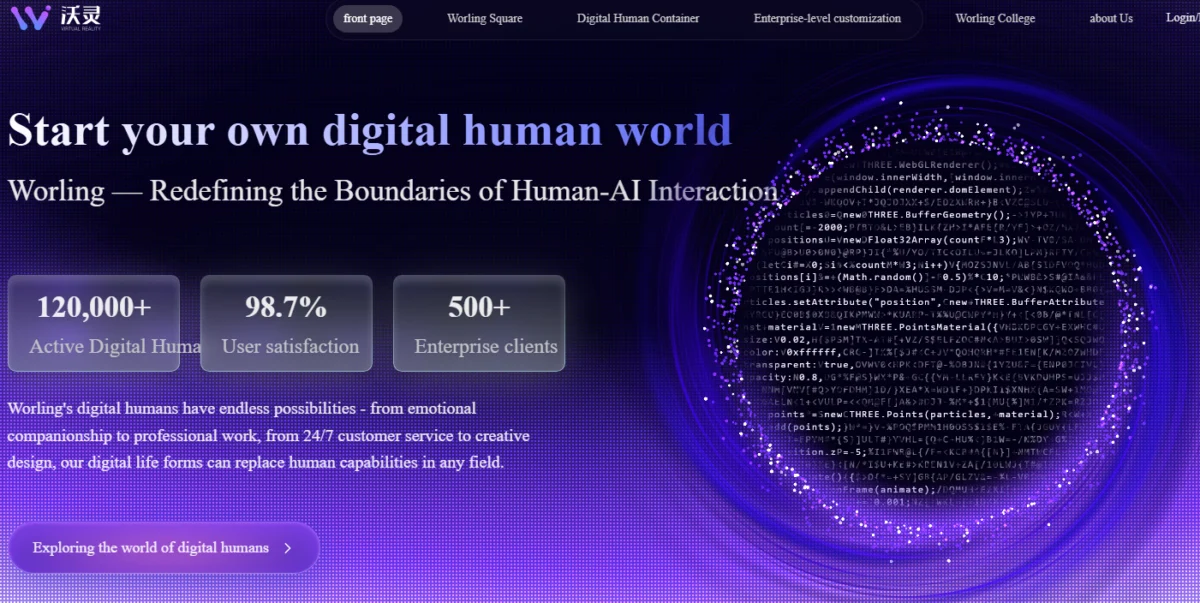
The operational hub of the enterprise, hosted at the domain fwgcloud[.]com, boldly claims that the company is "redefining the boundaries of human-AI interaction," boasting a fleet of over 120,000 rent-a-bot "AI digital humans" purportedly designed for emotional companionship, customer service, and creative design.
However, Bitsight’s investigation suggests this facade is primarily a smoke screen. The fwgcloud domain shares critical SSL certificate signatures with the domains commanding the phone-spoofing apps found on the H96 sticks.
The web properties generated by these apps consist of entirely machine-generated articles and graphics spanning finance, health, gaming, music, and food blogs. Intriguingly, rigorous traffic analysis confirmed that these AI-generated sites refused to display advertisements unless the visiting browser agent explicitly matched the spoofed mobile device profile transmitted by a compromised H96 streaming box.
Vision and Reasoning Systems
To circumvent advanced ad-fraud detection mechanisms deployed by digital advertisers, the Fengwo Group integrated sophisticated automation. When an H96 box is selected for a task, it receives a modular Blockly script instructing it to silently launch a web browser, navigate pages, manage active tabs, and interact with advertisements.
To ensure these actions mimic organic human behavior, the bot network fuses three separate vision and reasoning systems into a single interface. This allows the automated scripts to accurately distinguish advertisements from surrounding page layouts and navigate web interfaces just as a human user would.
The Dual-State Protocol: Proxy by Day, Fraud by Night
Perhaps the most ingenious engineering choice within the H96 botnet architecture is its resource management protocol. Bitsight observed that individual streaming boxes never performed residential proxy routing and ad fraud simultaneously.
TV On (HDMI Signal Active): When a user turns on their television and the box detects an active HDMI signal, the device pivots entirely to functioning as a residential proxy—relaying anonymous third-party internet traffic through the user’s home network.
TV Off (Standby Mode): When the television is powered down, the streaming box seamlessly switches out of proxy mode and resumes executing background ad-fraud routines.
Researchers deduce this separation of duties is essential: ad-fraud tasks are computationally heavy, and running them concurrently with video streaming would degrade device performance, tipping off the user that something is amiss.
Supporting Data and Financial Estimates
While the true financial scope of the Fengwo Group’s operations remains obscured by layered shell entities in Hong Kong and Singapore, Bitsight’s conservative telemetry models paint a lucrative picture:
Global Footprint: Bitsight tracked approximately 38,000 active streaming boxes phoning home to a single, older core domain operated by the Fengwo Group.
Daily Revenue: Based strictly on this isolated telemetry sample, researchers estimate that the ad-fraud network generates upwards of $50,000 per day in fraudulent ad-payouts.
The Proxy Revenue Stream: This $50,000 daily figure strictly represents ad-fraud monetization and excludes the substantial, parallel revenue collected by renting out residential IP bandwidth to data scrapers and cybercriminals.
The "Digital Human" Scale: While Fengwo claims 120,000 AI personalities, researchers suspect this number either reflects the true scale of their botnet hardware disguised in marketing language or serves as a deliberate obfuscation tactic to mask the volume of their underlying bot infrastructure.
Official Warnings and Industry Implications
The discovery of the Fengwo Group ad-fraud apparatus underscores a systemic regulatory and supply-chain failure within global e-commerce. Despite continuous, high-profile warnings issued by the Federal Bureau of Investigation (FBI) and cybersecurity alliances regarding compromised Internet of Things (IoT) hardware, major online retailers—including Amazon, Best Buy, and Newegg—continue to list hundreds of uncertified Android streaming devices.
+-------------------------------------------------------------------------+
|                      THE CONSUMER THREAT CYCLE                          |
|                                                                         |
|  [Cheap Uncertified TV Box Purchased Online]                            |
|                        |                                                |
|                        v                                                |
|  [Pre-Installed Backdoors & Proxy Software Activated]                   |
|                        |                                                |
|         +--------------+--------------+                                 |
|         |                             |                                 |
|         v                             v                                 |
|   [TV IS ON]                  [TV IS OFF]                               |
|   Residential IP Rented       AI-Driven Ad Fraud                        |
|   Out to Anonymous            Executed via Spoofed                      |
|   Third Parties               Mobile Phone Profiles                     |
+-------------------------------------------------------------------------+
The Insecurity of Unvetted IoT Hardware
These generic, inexpensive streaming boxes are shipped with outdated firmware, gaping security vulnerabilities, and zero default authentication. Threat actors routinely exploit these weaknesses to build expansive botnets—such as the massive Kimwolf botnet documented by proxy-tracking firm Synthient earlier this year—which enslaved millions of unvetted consumer devices.
Furthermore, the threat extends far beyond television accessories. Industry investigations have revealed that residential proxy software and malicious payloads are increasingly being pre-installed across a wide array of popular consumer electronics, most notably digital photo frames and smart home appliances.
Direct Response Failures
Efforts by security researchers to seek accountability from the perpetrators have hit predictable brick walls. When KrebsOnSecurity attempted to contact the Fengwo Group via the designated corporate email address (postmaster@fwgcloud[.]com), incoming inquiries bounced back with automated error messages indicating that the company’s mailbox was permanently full due to overwhelming volume.
Mitigation and Consumer Protection
As cybercriminal syndicates grow increasingly adept at weaponizing consumer hardware, cybersecurity experts emphasize that vigilance starts at the point of purchase and extends to network hygiene.
Stick to Reputable Brands: Consumers are strongly advised to avoid generic, unbranded streaming sticks found on discount e-commerce listings. Major name-brand manufacturers maintain stricter firmware integrity and security patch schedules.
Verify Android TV OS Certification: Google provides official support guidelines allowing users to verify whether a streaming device runs genuine, Play Protect-certified Android TV software.
Audit Installed Applications: Unofficial apps downloaded from third-party repositories frequently bundle hidden proxy or ad-fraud frameworks. Users should regularly audit their app inventories.
Consult Threat Trackers: Research firms such as Synthient maintain public databases—including community-sourced CSV manifests on GitHub—listing known consumer IoT devices compromised by pre-installed proxy and botnet software.
As long as online marketplaces permit the frictionless sale of unvetted, bargain-priced smart hardware, operations like the Fengwo Group will continue to convert unwitting households into silent partners in global cybercrime.

 By Nana Muazin


 Evan Lee Salim
 Neng Nana
 rifanmuazin
